> For the complete documentation index, see [llms.txt](https://docs.ilert.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.ilert.com/integrations/inbound-integrations/crowdstrike.md).
# CrowdStrike Integration
Integrate CrowdStrike threat alerts with ilert to instantly convert endpoint detection events into incidents and accelerate response.
By connecting CrowdStrike with ilert, endpoint threat detections – like malware alerts or suspicious behavior – automatically generate actionable incidents. This enables rapid notification, structured escalation, and centralized incident tracking, strengthening your endpoint security response.
## In ilert: Create a CrowdStrike alert source
1. Go to **Alerting** → **Alert sources** and click **Create new alert source**.
2. Search for **CrowdStrike**, click its tile, and click **Next**.
3. Give your alert source a name, optionally assign teams, and click **Next**.
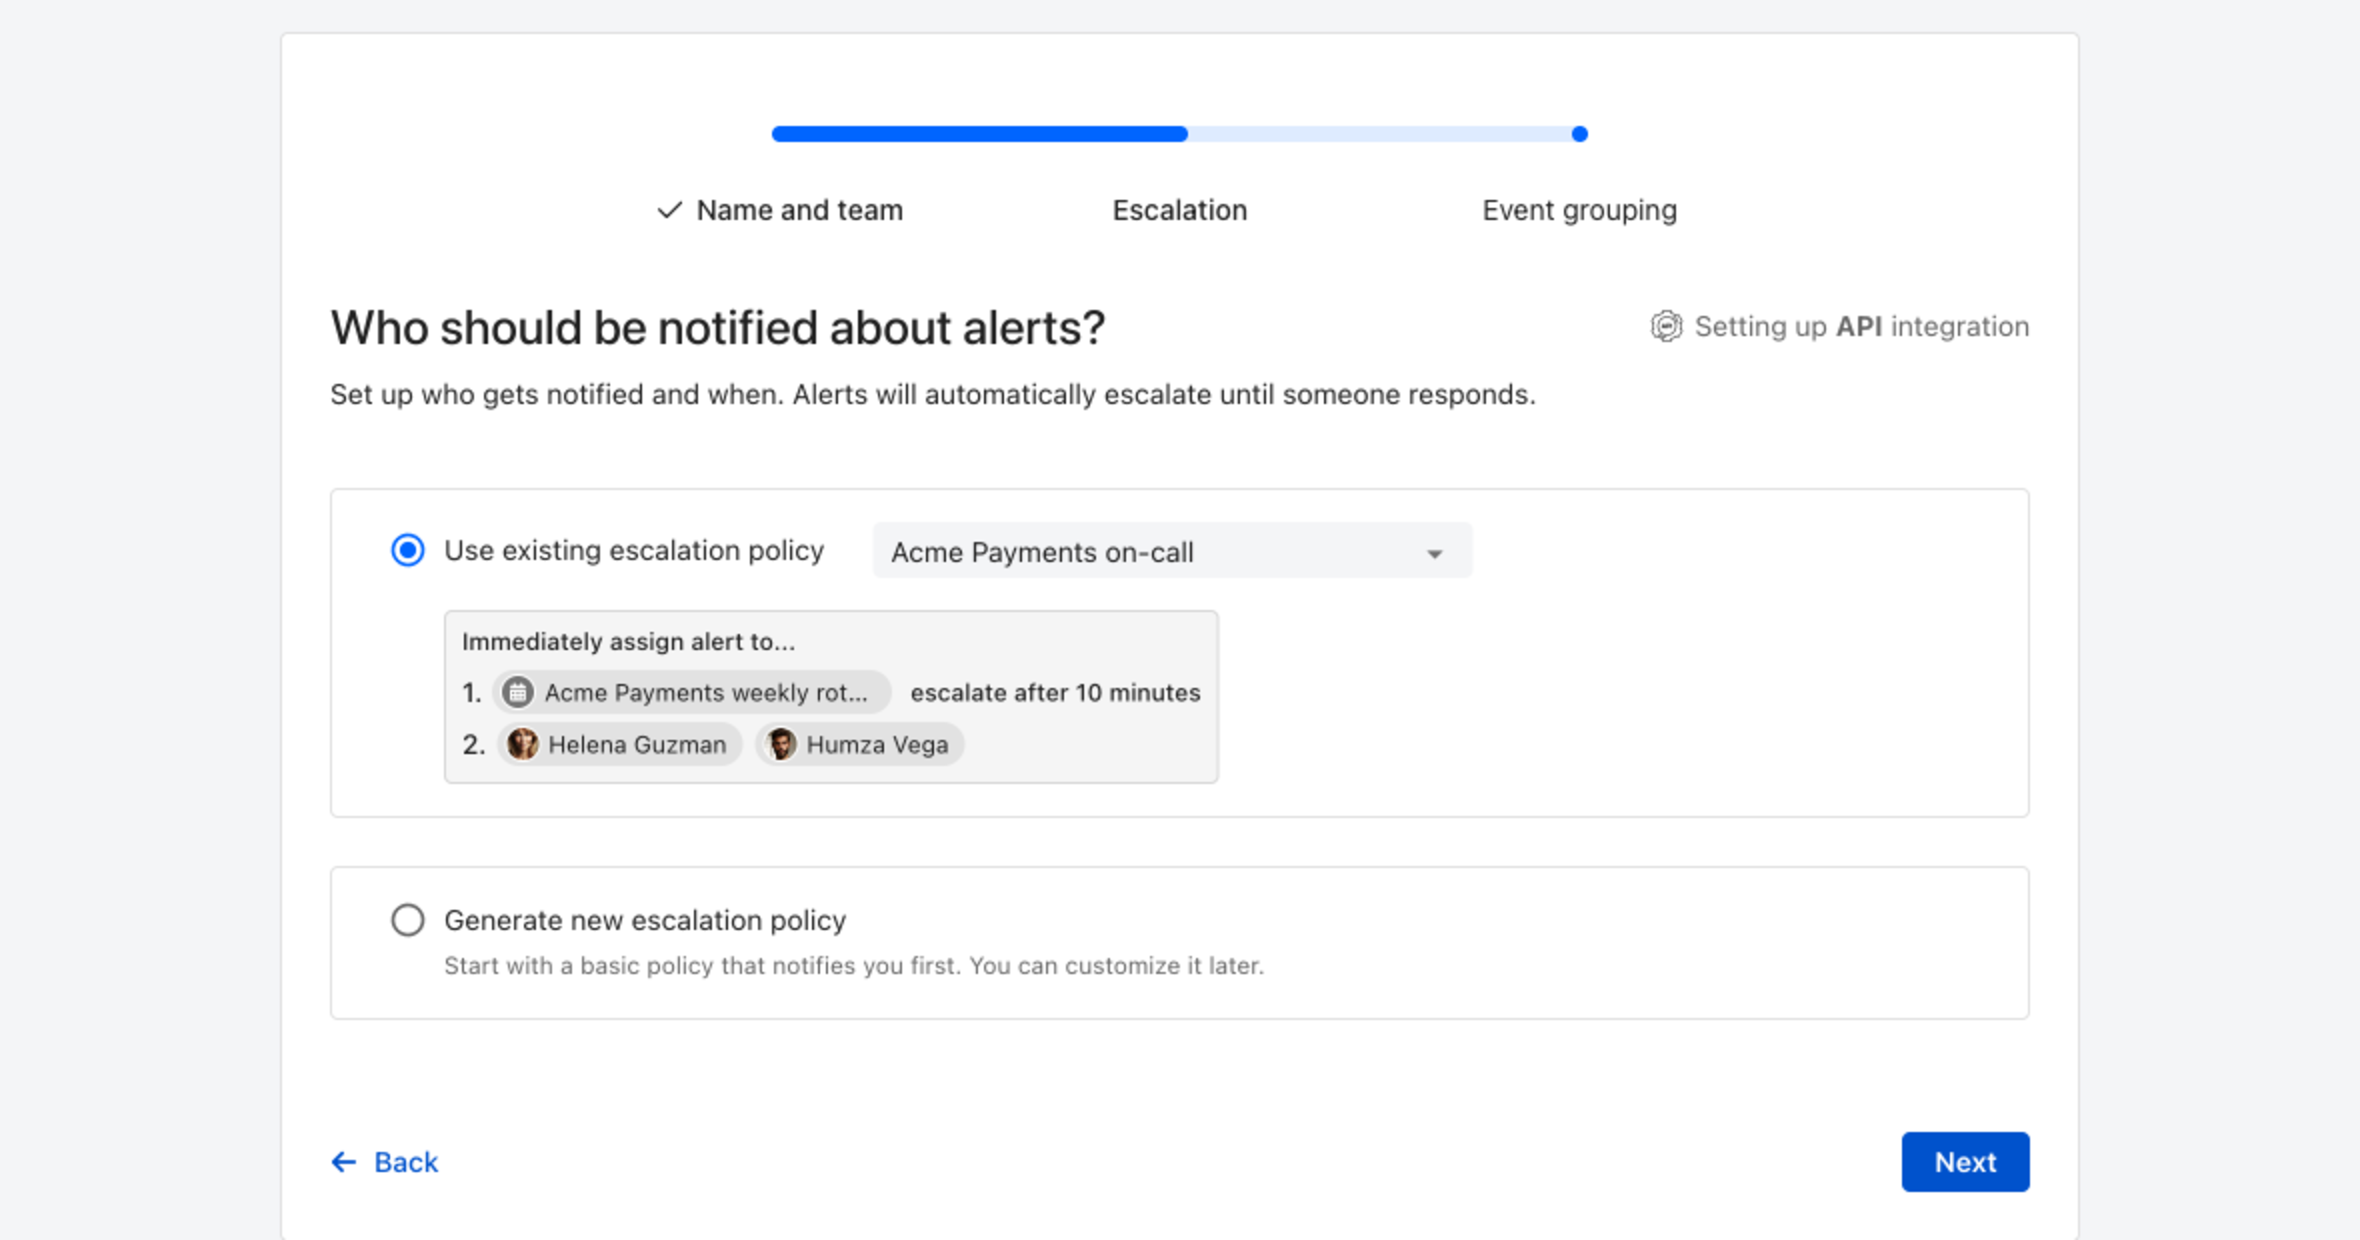
4. Choose who gets notified: select **Use existing escalation policy** and pick a policy, or **Generate new escalation policy** to start with a basic one that notifies you first. Click **Next**.
Pick an existing escalation policy, or generate a basic one without leaving the wizard.
5. Select **Default grouping** and click **Continue setup**. It groups events by the alert key the integration sets; the other [grouping options](/alerting/configure-alerting/alert-sources.md#event-grouping) are easier to judge once events are arriving.
6. The next page shows more settings, such as notification priority and alert templates. Click **Finish setup** for now; you can change them later.
7. On the final page, ilert shows the integration key and URL for this alert source. You will need them later in this guide.
## In CrowdStrike
1. Go to Workflows Dashboard by clicking the "**CrowdStrike**" logo on top left and choose **Workflows**

2. Click on **Create a Workflow** on top right, on the workflow workspace add a trigger, and choose "**New Detection"** additionally you can also add Condition, in this case we chose greater than **Medium** severity

3. On creating Action choose Action type **Notification** and **Call webhook** as Action, you might need to configure it from store if you haven't done so. Go ahead and click the Store link, and click "**Configure**" on the Webhook.
4. Add the **Name** in this case we name it as ilert-incident and put the **Webhook URL** that we got from ilert's dashboard earlier.

5. Click **Save Configuration**, and it should be added to the Workflow workspace.
6. Choose the Webhook name based on the name that we set earlier, and choose **ALL** Data to include

7. Save the configuration and turn the workflow on, and upon Detection creation, the incident will be created on ilert.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://docs.ilert.com/integrations/inbound-integrations/crowdstrike.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.